AI Governance Software

Riskonnect’s AI Governance software helps you apply a structured methodology to demonstrate control of AI use – without limiting innovation.

Use AI with confidence. Minimize risk by maintaining proactive, real-time oversight as AI scales across the organization.

Prove AI compliance – and avoid penalties. Automate governance processes, maintain audit-ready records, and align with evolving regulations.

Ensure AI integrity and accountability. Centralize AI risk detection so teams across the organization – legal, procurement, security, etc. – can quickly determine if AI supports or threatens business goals.
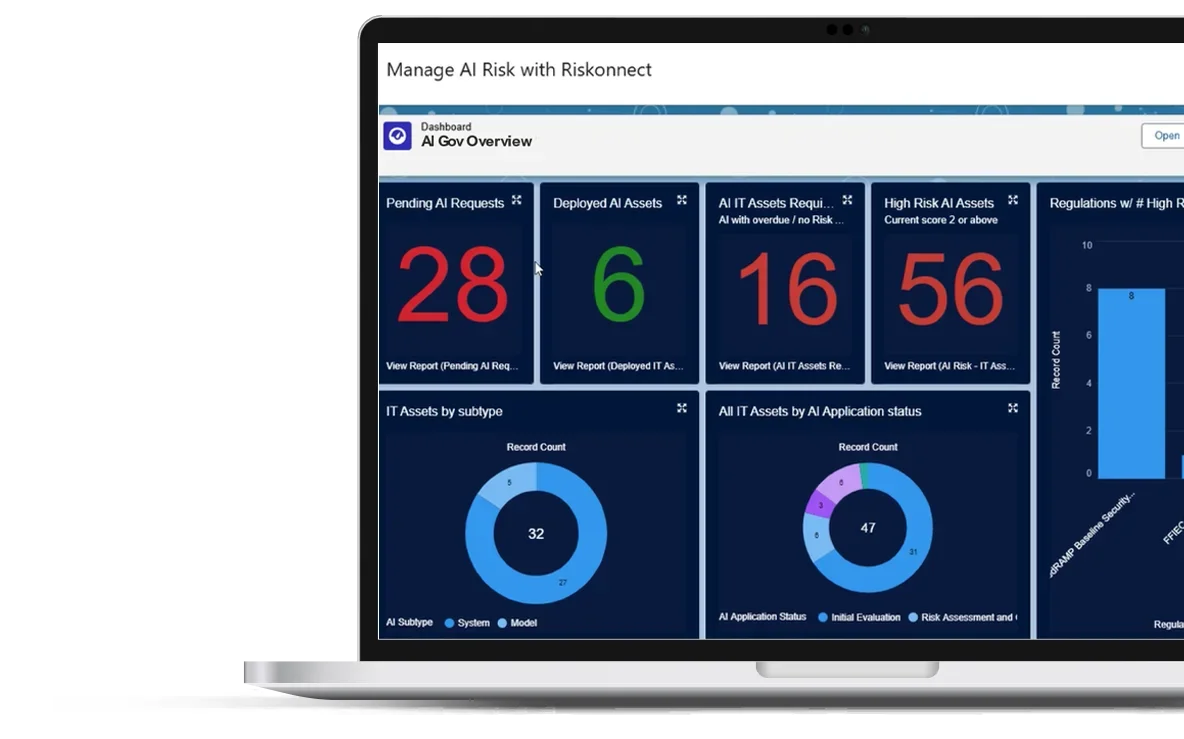
AI governance software demo

AI Governance

Platform Highlights

  • Regulatory
    Compliance Frameworks
    Instantly apply preloaded regulations and frameworks, including the EU AI Act, GDPR, ISO 42001, and NIST AI RMF.
  • Governance Policy
    Configuration
    Customize and enforce AI policies that align with internal and external requirements.
  • Audit
    Management
    Maintain a record of AI decisions and actions for transparency and compliance.
  • AI Asset Lifecycle
    Management
    Oversee development, deployment, updates, and retirement of AI systems within a governed framework.
  • AI Monitoring
    Track performance trends, drift, and unexpected behavior to catch issues before they escalate.
  • Control
    Monitoring
    Implement controls to verify data models, and check for bias and accuracy across AI models.
  • Approval
    Workflows
    Track AI-usage requests through prebuilt workflows to ensure responsible innovation.
  • Risk Analytics
    and Insights
    Easily customize your reporting and dashboards to tell your story and inform decisions. Learn more.

Confidently Comply

with AI Regulations

Worried about incurring penalties for accidentally violating evolving AI regulations? Riskonnect’s AI Governance software comes preloaded with frameworks and regulatory standards to help you stay ahead of compliance requirements, so you can focus on innovation — not red tape.

  • Leverage built-in regulations and frameworks like the EU AI Act, GDPR, ISO 42001, and NIST AI RMF.
  • Run automated audits to ensure transparency and accountability across AI systems.
  • Tailor governance policies to align with industry-specific risks and organizational needs.
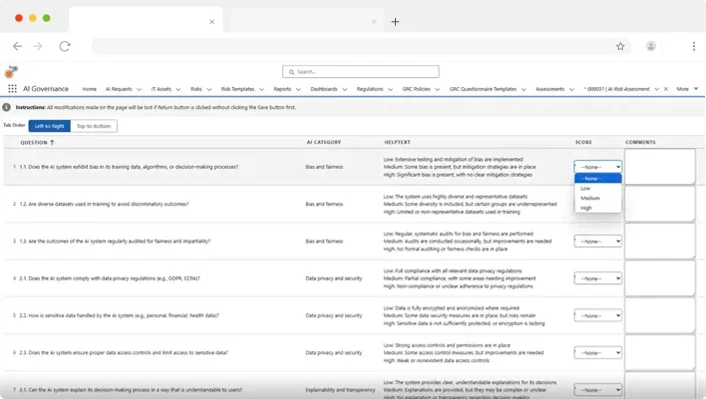
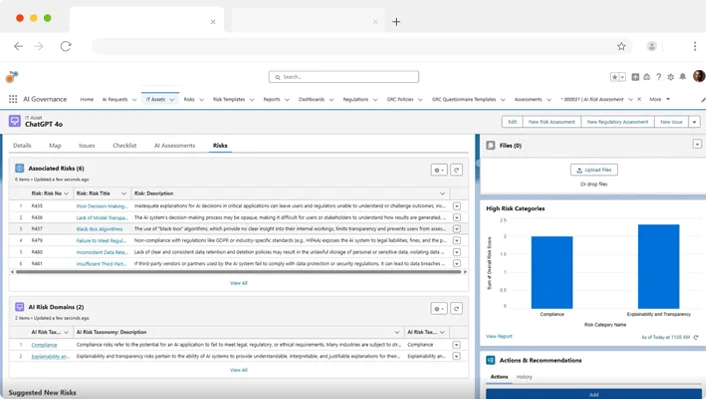
Riskonnect AI governance tool UX
Riskonnect AI governance software UX

Proactively Manage
AI Risk and Ethics

Can you identify bias in AI output before it causes harm? Riskonnect’s AI Governance software continuously monitors your AI systems for ethical integrity, compliance, and assurance, giving you the insight to act before risks escalate into problems.

  • Conduct control testing to detect bias, model drift, and anomalies early.
  • Trigger automated alerts when deviation or compliance risks arise.
  • Score AI risk and build mitigation plans to ensure reliable governance outcomes.

Scale AI Across

the Enterprise without Fear

Are you equipped to effectively govern AI as usage scales? Riskonnect’s AI Governance software provides the structure and visibility to allow safe experimentation and adoption across departments and geographies — all from a single platform.

  • Manage the full AI model lifecycle with built-in version control.
  • Access real-time dashboards for a clear, enterprise-wide view of AI governance.
  • Integrate seamlessly with enterprise risk management systems to unify oversight.
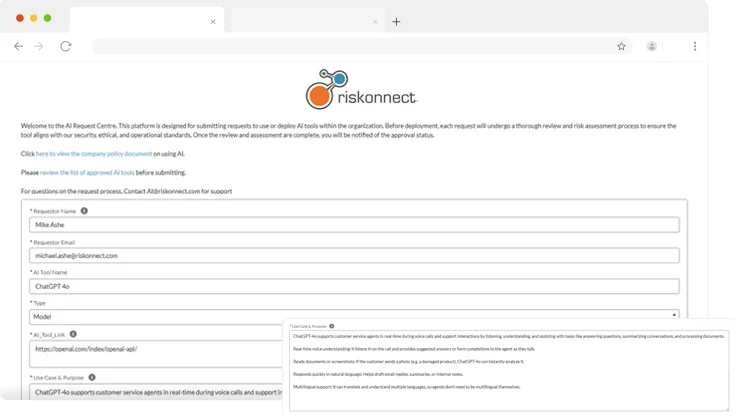
Riskonnect AI governance platform UX

Get Started with These Helpful Resources
How Organizations Are Using AI to Manage Risk
ARTICLE
How Organizations Are Using AI to Manage Risk
This article reveals the most popular uses of AI in risk management and common gaps in governance – all backed by data.
Compliance at the Speed of Change
WEBINAR
Compliance at the Speed of Change: Modernizing GRC for the AI Era.
Replay this webinar for practical insights on how unified compliance supports confident decisions in the era of AI.
From Black Box to Building Blocks
WEBINAR
Operationalizing AI Governance Through GRC
Replay this webinar to find out how to expand your current GRC program to include AI risks, while keeping complexity in check and innovation on track.

Customers with Enhanced
AI Governance Programs Also Use

IT Risk Management
Identify your top IT, cyber, operational resilience, and other technology risks to minimize the financial impact.
Third-Party
Risk Management
Collect all vendor information – including agreements, contracts, policies, and access credentials – into one place to efficiently monitor suppliers throughout the entire relationship.
Compliance
Aggregate all corporate and legal policies, procedures, and requirements from across the organization into one centralized location.

Start anywhere. Expand everywhere.

Industry Recognition for Riskonnect
Redhand Advisors Gartner Wheelhouse Advisor

Start partnering with Riskonnect today.
Find out how Riskonnect can transform the way you view risk.

Your AI Governance Questions Answered

AI governance is the structured set of policies, processes, controls, and oversight mechanisms that organizations use to ensure their AI systems are used responsibly, transparently, and in compliance with applicable regulations and ethical standards. As AI adoption accelerates across industries — automating decisions in hiring, lending, healthcare, customer service, fraud detection, and more — the risks associated with uncontrolled AI use have grown proportionally: regulatory penalties, algorithmic bias causing discriminatory outcomes, model drift producing unreliable results, data privacy violations, and reputational damage from AI failures that weren’t caught before they became public. AI governance matters now because regulators in multiple jurisdictions are moving from guidance to enforceable requirements — and because organizations that fail to demonstrate structured oversight of their AI systems are taking on risks they may not fully see.
An AI governance platform gives organizations structured visibility and control over how AI systems are developed, deployed, monitored, and retired across the entire enterprise. It provides the tools governance teams need to maintain an inventory of AI assets, ensure compliance with regulatory frameworks, enforce policies, monitor AI models for bias and drift, manage approval workflows for new AI use cases, and maintain the audit-ready records that regulators increasingly require. The goal is to enable organizations to adopt and scale AI with confidence — not by slowing innovation, but by ensuring that AI use is tracked, tested, and demonstrably within defined risk and compliance boundaries. Without this structure, AI use tends to proliferate informally across departments, creating compliance exposure and risk that no one has full visibility into.
The regulatory landscape for AI is developing rapidly, with several frameworks and regulations already in force or approaching enforcement. The EU AI Act is the most comprehensive — a risk-tiered regulatory framework that classifies AI systems by their potential for harm and imposes obligations ranging from transparency requirements for limited-risk systems to stringent conformity assessments and human oversight requirements for high-risk systems. GDPR applies to AI systems that process personal data, imposing requirements for transparency, data minimization, and automated decision-making safeguards. ISO 42001 is the international standard for AI management systems, providing a structured framework for organizations seeking to demonstrate governance maturity. The NIST AI Risk Management Framework (AI RMF) is a voluntary US framework that provides comprehensive guidance on identifying, measuring, and managing risk across the AI lifecycle. Riskonnect’s platform comes preloaded with all four of these frameworks, enabling organizations to map their AI systems to applicable requirements without building compliance mappings from scratch.
Model drift refers to the degradation in an AI model’s performance or predictive accuracy over time, caused by changes in the real-world data the model encounters compared to the data it was trained on. A fraud detection model trained on pre-pandemic transaction patterns, for example, may become less accurate as consumer behavior shifts. A credit risk model trained on one economic environment may systematically misclassify borrowers when conditions change. From a governance perspective, drift is a significant risk because it means an AI system that was validated and approved at deployment may be producing unreliable or biased outputs months later — potentially making consequential decisions based on outdated assumptions without anyone detecting the problem. AI governance solutions address this through continuous monitoring of model performance metrics, real-time alerts when drift indicators cross defined thresholds, and documented evidence that monitoring is occurring — which is increasingly what regulators expect to see.
Algorithmic bias occurs when an AI model produces systematically unfair or discriminatory outputs — for example, consistently under-approving loan applications from certain demographic groups, or rating job candidates differently based on factors that correlate with protected characteristics. Bias can be introduced at multiple points: through imbalanced training data, through proxy variables that correlate with protected attributes, or through feedback loops that amplify historical disparities. Detecting bias requires testing model outputs across different demographic groups and comparing outcomes statistically to identify patterns that can’t be explained by legitimate predictive factors. AI governance platforms support bias detection through control testing that checks model outputs for fairness across relevant dimensions, flags anomalies for investigation, and maintains documentation of testing results that can be provided to regulators or auditors. The goal is to catch bias before it causes harm — rather than discovering it after a regulatory complaint or public incident.

The AI asset lifecycle covers the full progression of an AI system from initial development through deployment, ongoing operation, updates, and eventual retirement. Each stage carries distinct governance requirements: development requires validation that the model performs as intended and doesn’t exhibit bias; deployment requires approval workflows and documented risk assessments; ongoing operation requires monitoring for drift, bias, and unexpected behavior; updates require re-validation to ensure changes don’t introduce new risks or policy violations; and retirement requires managed decommissioning that ensures data handling obligations are met. Without a structured approach to AI lifecycle management, AI usage proliferates across the organization with incomplete documentation, inconsistent oversight, and no clear accountability for what the platforms are used for or who owns them. Riskonnect’s AI Asset Lifecycle Management capability tracks AI systems through each stage within a governed framework, maintaining version control and the documentation trail that internal audit and external regulators expect.

An AI inventory is a comprehensive, maintained record of all AI systems in use across the organization — what they do, where they’re deployed, what data they use, who owns them, what their risk classification is under applicable frameworks, and what governance controls are applied to each. Most organizations that have been adopting AI informally for several years would be surprised to discover how many AI-enabled systems are in use across departments — ranging from enterprise tools with embedded AI features to custom-built models developed by data science teams. Without an inventory of every model and system, it’s impossible to demonstrate compliance with regulations like the EU AI Act that require organizations to identify which of their systems fall into regulated categories. Riskonnect’s platform supports AI inventory management as the foundation of the governance program — making sure organizations know what they’re governing before they try to govern it.
AI governance doesn’t exist in isolation from the organization’s existing technology risk and compliance programs. An AI system that processes personal data is subject to data privacy controls managed by the compliance team. An AI system with access to critical IT infrastructure is a technology risk that belongs in the IT risk register. Procurement of third-party AI tools introduces vendor risk that should be assessed through the TPRM program. When AI governance solutions are integrated with IT risk management, compliance, and the broader GRC platform, AI risks are visible within the organization’s overall risk picture rather than managed as a separate, isolated program. Riskonnect’s AI Governance capability connects AI oversight with the broader enterprise risk and compliance environment, bringing governance, risk, and compliance together in one platform. For more on how AI and GRC intersect, see AI Governance: 5 Ways to Embed AI Oversight into GRC.

AI approval workflows are the structured review and sign-off processes that govern when and how new AI use cases are approved for deployment. Without formal workflows, AI adoption tends to happen informally — a team discovers a new AI tool, starts using it, and only retrospectively considers whether it is compliant with data privacy requirements, introduces regulatory risk, or aligns with the organization’s AI policies. Governance software addresses this by routing AI usage requests through defined approval steps: risk assessment, compliance review, legal review for high-risk applications, security assessment, and executive sign-off where required. Each step is documented, creating an audit trail that demonstrates the organization applied appropriate scrutiny before allowing AI to be deployed. Riskonnect’s prebuilt approval workflows can be customized to reflect the organization’s specific governance requirements and compliance obligations — providing structure without creating unnecessary friction for lower-risk AI use cases.

The evaluation should start with your current state: How much AI is already in use across the organization, how much visibility do you have into it, and what regulatory obligations are you facing? Organizations subject to the EU AI Act need software that supports the Act’s risk classification framework and conformity assessment requirements. Organizations with significant data privacy obligations need tight integration between AI governance and their data governance program. Key evaluation criteria include: preloaded support for the legal frameworks that apply to your organization; AI inventory management to establish the foundation of governance; lifecycle management across development, deployment, monitoring, and retirement; continuous monitoring for drift and bias with real-time alerting; approval workflow configurability; audit trail and record-keeping for regulatory examination; and integration with existing GRC, IT risk, and compliance programs. For a broader view of how AI fits into the GRC landscape, see Integrating AI into GRC.
AI agents and agentic AI can introduce additional governance considerations because they may interact with systems, access data, and take actions with varying degrees of autonomy. Unlike AI systems that primarily generate outputs for a human to review, AI agents may initiate autonomous actions or decisions within defined workflows, making visibility, permissions, oversight, and accountability particularly important. Effective agent governance should consider how agents are developed and deployed, what data and systems they can access, what actions they are permitted to take, and how their activity is monitored and documented. Governance controls can help enterprises assess agent-related risk, enforce policies, monitor behavior, and maintain audit-ready evidence throughout the AI lifecycle. This enables organizations to adopt agentic AI responsibly while maintaining appropriate oversight as AI use scales across the enterprise.